IGEL Blog
Five Takeaways from the Demo Village at IGEL Now & Next Melbourne
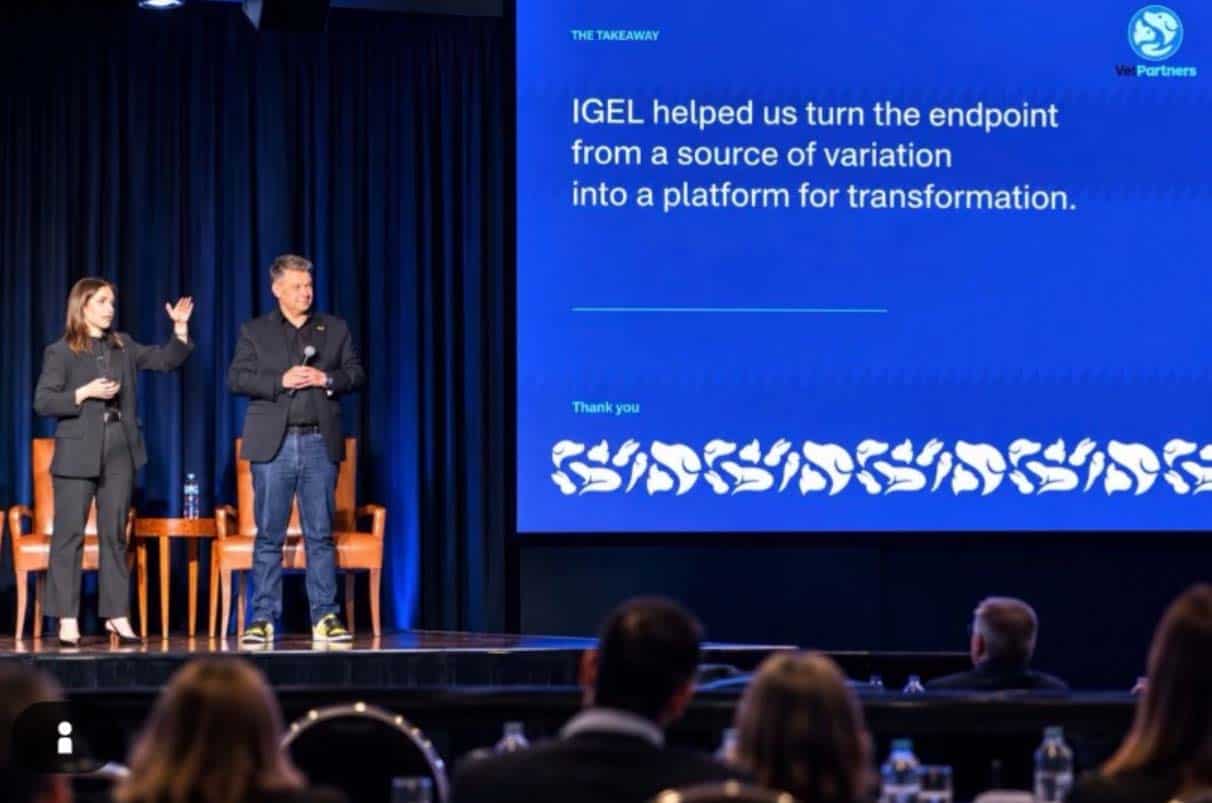
More than 150 customers, partners, vendors, consultants and students joined us in Melbourne for the IGEL Now & Next Workspace & Endpoint Security Summit. The customer presentations were a real highlight. They shared the use cases they are addressing, the experience for end users, the architectural choices behind their approach, and the operational and cost outcomes they are working towards. Hearing that directly from customers gave the day a practical perspective that went well beyond the technology itself.
I spent much of the day in the Demo Village alongside Gordon Cass and Adrian Caceres.
For me, that was one of the strongest themes of the day: customers were not simply looking at individual features. They were immediately mapping what they saw to real problems in their own environments.
The demos became starting points for wider conversations about architecture, integration, legacy workloads, business continuity and the role of the endpoint in a broader workspace strategy.
If you couldn’t join us in Melbourne, here are my five takeaways from the Demo Village.
1. The partner ecosystem matters
One of the demos brought together IGEL, Imprivata and Omnissa.
The experience itself was simple: tap a badge, authenticate into a Windows desktop delivered through Omnissa Horizon, move to another endpoint and reconnect to the session.
But the more important point was what sat behind that experience.
No single product delivered the complete workflow. It came from different technologies working together around a common use case. IGEL provided the secure endpoint foundation, while Imprivata and Omnissa brought capabilities around authentication, session management and workspace delivery.
Healthcare customers immediately recognised the use case, but we also discussed similar requirements in aviation and other environments where workstations are shared and users need to move between locations.
The takeaway was not really about badge authentication. It was about how well the endpoint can participate in an architecture that already includes multiple platforms and vendors.
Customers rarely have the luxury of starting from a blank page. The value of an ecosystem is its ability to work with the investments they already have.
2. Windows can be a workload rather than the endpoint strategy
Another demo showed a Windows virtual machine running locally on an IGEL OS endpoint using IGEL Managed Hypervisor.
This generated some interesting conversations around operational technology, specialised applications and legacy Windows workloads.
Several people described situations where an application still requires Windows but does not necessarily justify a complete VDI environment or an immediate application migration.
That led to a useful question:
Does the endpoint need to be Windows, or does the workload simply need Windows?
For some environments, running that workload locally in a virtual machine creates another architectural option, while IGEL OS remains the operating system on the endpoint.
The discussion was less about virtualisation itself and more about finding practical ways to modernise without pretending that every legacy dependency can disappear overnight.
A credible modernisation strategy has to meet organisations where they are. It should reduce risk and create options while allowing essential workloads to continue operating.
3. Business continuity must include the endpoint
IGEL Business Continuity & Disaster Recovery probably generated the most questions in the Demo Village.
People wanted to understand what happens during an incident, what happens to Windows, how endpoints are transitioned and how this capability fits into an existing incident response process.
With IGEL BC&DR Emergency Mode, administrators can centrally reboot supported IGEL Dual Boot-enabled endpoints into IGEL OS. The Windows environment is bypassed and preserved while users reconnect to approved applications and services.
The conversations quickly moved beyond the technology itself.
Organisations invest significant time in planning how to recover infrastructure, applications, identity and data. But the endpoint and the user’s ability to resume work can still be a gap.
Even if the rest of the environment is available, what does the user actually work from while investigation and recovery are still underway?
That is the more important architectural question. Business continuity is not complete until people can securely access the services they need.
4. Digital signage does not have to become another management silo
We also had a hospital digital signage example running on relatively modest hardware.
It was one of the simpler demos, but it raised a valuable operational question.
Special-purpose devices such as digital signage are often treated as a separate environment, with their own hardware, configuration and management approach. Over time, those separate environments can add cost and operational complexity.
The demo showed another option: deliver the signage experience through IGEL OS and manage those endpoints as part of the wider estate.
For hospitals, campuses and other distributed environments, the interesting point was not really the signage itself.
It was whether every specialised endpoint use case genuinely needs another management silo.
Sometimes the greatest operational improvement comes not from adding a new capability, but from bringing an existing use case into a consistent and supportable management model.
5. Identity is beginning to shape the workspace
Another part of the Demo Village focused on identity, single sign-on and persona-based desktop experiences.
With IGEL Contextual Access and Persona Profiles, identity and role information can help determine which applications and configurations are presented when someone signs into an IGEL OS device.
That changes how we can think about endpoint configuration.
Instead of the experience being defined entirely by the physical device, it can increasingly reflect the person using it and the role they perform.
This prompted discussions about browsers, progressive web apps, native applications and virtual desktops coexisting on the same endpoint, while different users receive the workspace appropriate to their role.
For me, this is about more than personalisation. It represents a move from a purely device-centric model towards an identity-aware workspace, where access and experience can follow the user without requiring a different desktop design for every scenario.
Where do we go from here
The Demo Village gave people something tangible to work from. But the most valuable part of the day was seeing how quickly the discussions moved from features to architecture and real customer requirements.
Could this provide a practical path forward for a legacy Windows dependency?
Where does endpoint recovery fit into the incident response plan?
Can specialised devices become part of the same management model?
Can identity shape the workspace instead of IT building a different desktop for every use case?
These were the questions customers, partners and practitioners were asking in Melbourne.
They also reinforced something Adrian, Gordon and I see from different points in the customer journey: the best technical conversations do not begin with a product. They begin with the environment the customer already has, the constraints they are working within and the outcome they need to achieve.
If any of these questions sound familiar, bring us the use case. Talk to your local IGEL team, and let’s work through it together.
Related Posts